PROJECTS

Security Tooling · Lab Builds · Research

Things I build to break, defend, and understand systems.

root@kernellis:~# ls -la /opt/projects

[ 00 ]

HOME LAB

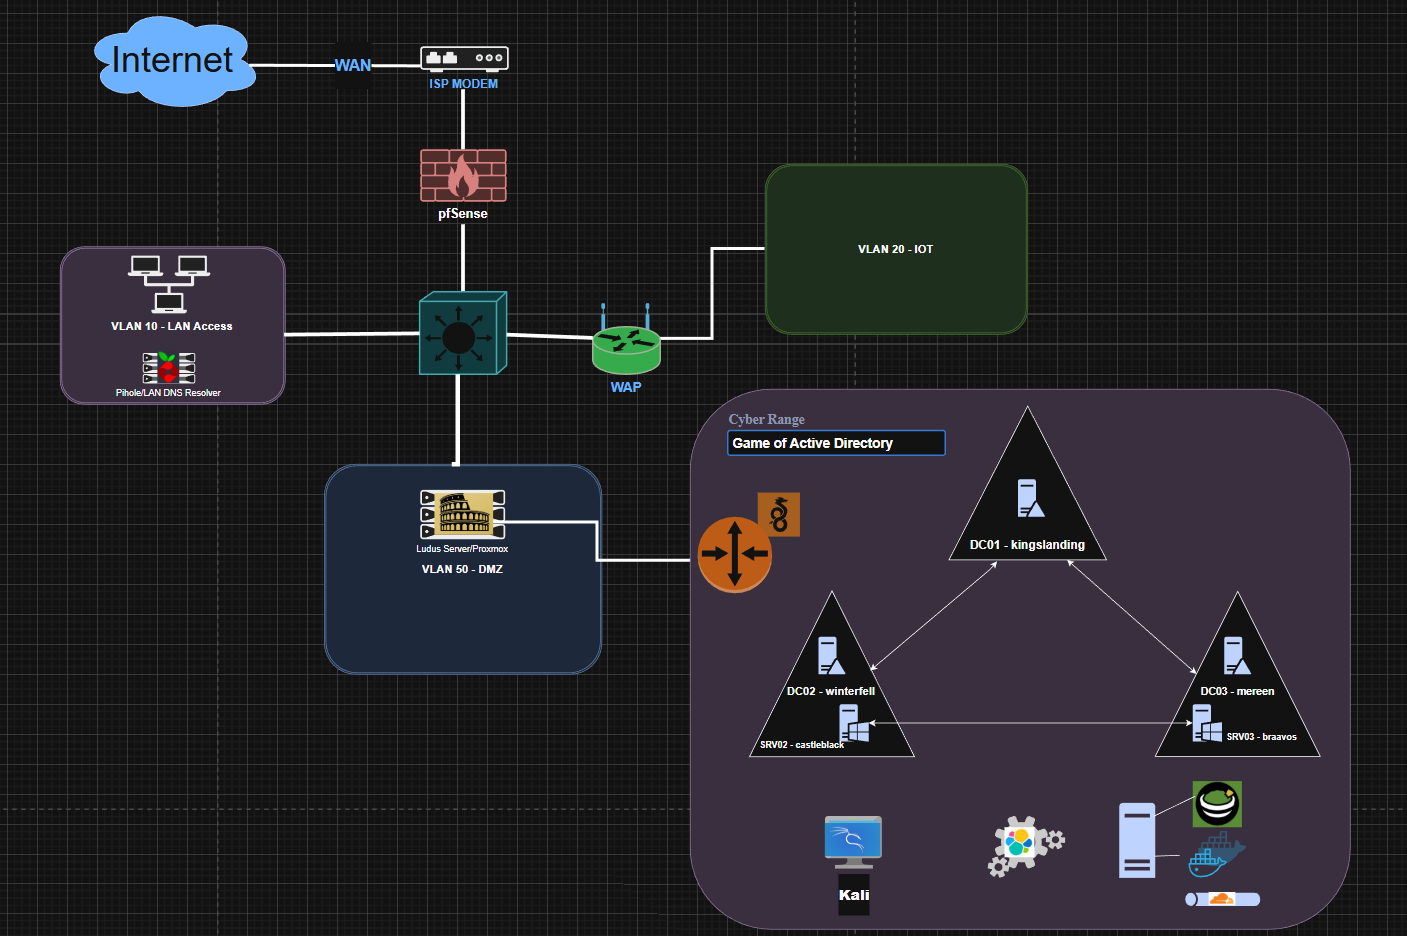
Segmented pfSense network behind the ISP edge: VLAN 10 for trusted LAN and a Pi-hole resolver, VLAN 20 for IoT, VLAN 50 as a DMZ running a Ludus/Proxmox host. The DMZ fronts a cyber range — a “Game of Active Directory” forest of three DCs and member servers, with Kali and a container-based detection stack pointed at it.

Home lab network diagram: the internet reaches an ISP modem, then a pfSense firewall feeding a core switch. The switch serves VLAN 10 (LAN workstations and a Pi-hole DNS resolver), VLAN 20 (IoT, via a wireless access point) and VLAN 50 (DMZ, a Ludus/Proxmox server). The DMZ connects through a router to a cyber range holding a Game of Active Directory forest — domain controllers kingslanding, winterfell and mereen with member servers castleblack and braavos — plus a Kali box and containerised tooling.
Network topology — edge, VLAN segmentation, and the AD cyber range.
  • pfSense
  • VLANs
  • Proxmox
  • Ludus
  • Active Directory
  • Detection

[ 01 ]

PROJECT ONE

Short description of what it does and why it exists. One or two sentences is plenty — the write-up carries the detail.

  • Python
  • Recon
  • CLI

root@kernellis:~# cat /opt/projects/README

  • Public source lives on GitHub — swap this for your profile URL.
  • Longer technical breakdowns live under write-ups.
  • Lab infrastructure runs at kernellis.online.